Safety Instrumented System Independence: Are Yours Really Separate?
Plant managers live with an invisible tension: keeping production running on the basic process
control system while relying on the safety instrumented system to prevent catastrophe. Safety
instrumented system independence is the property that makes the second half of that sentence true
— and the one most easily lost without anyone deciding to lose it.
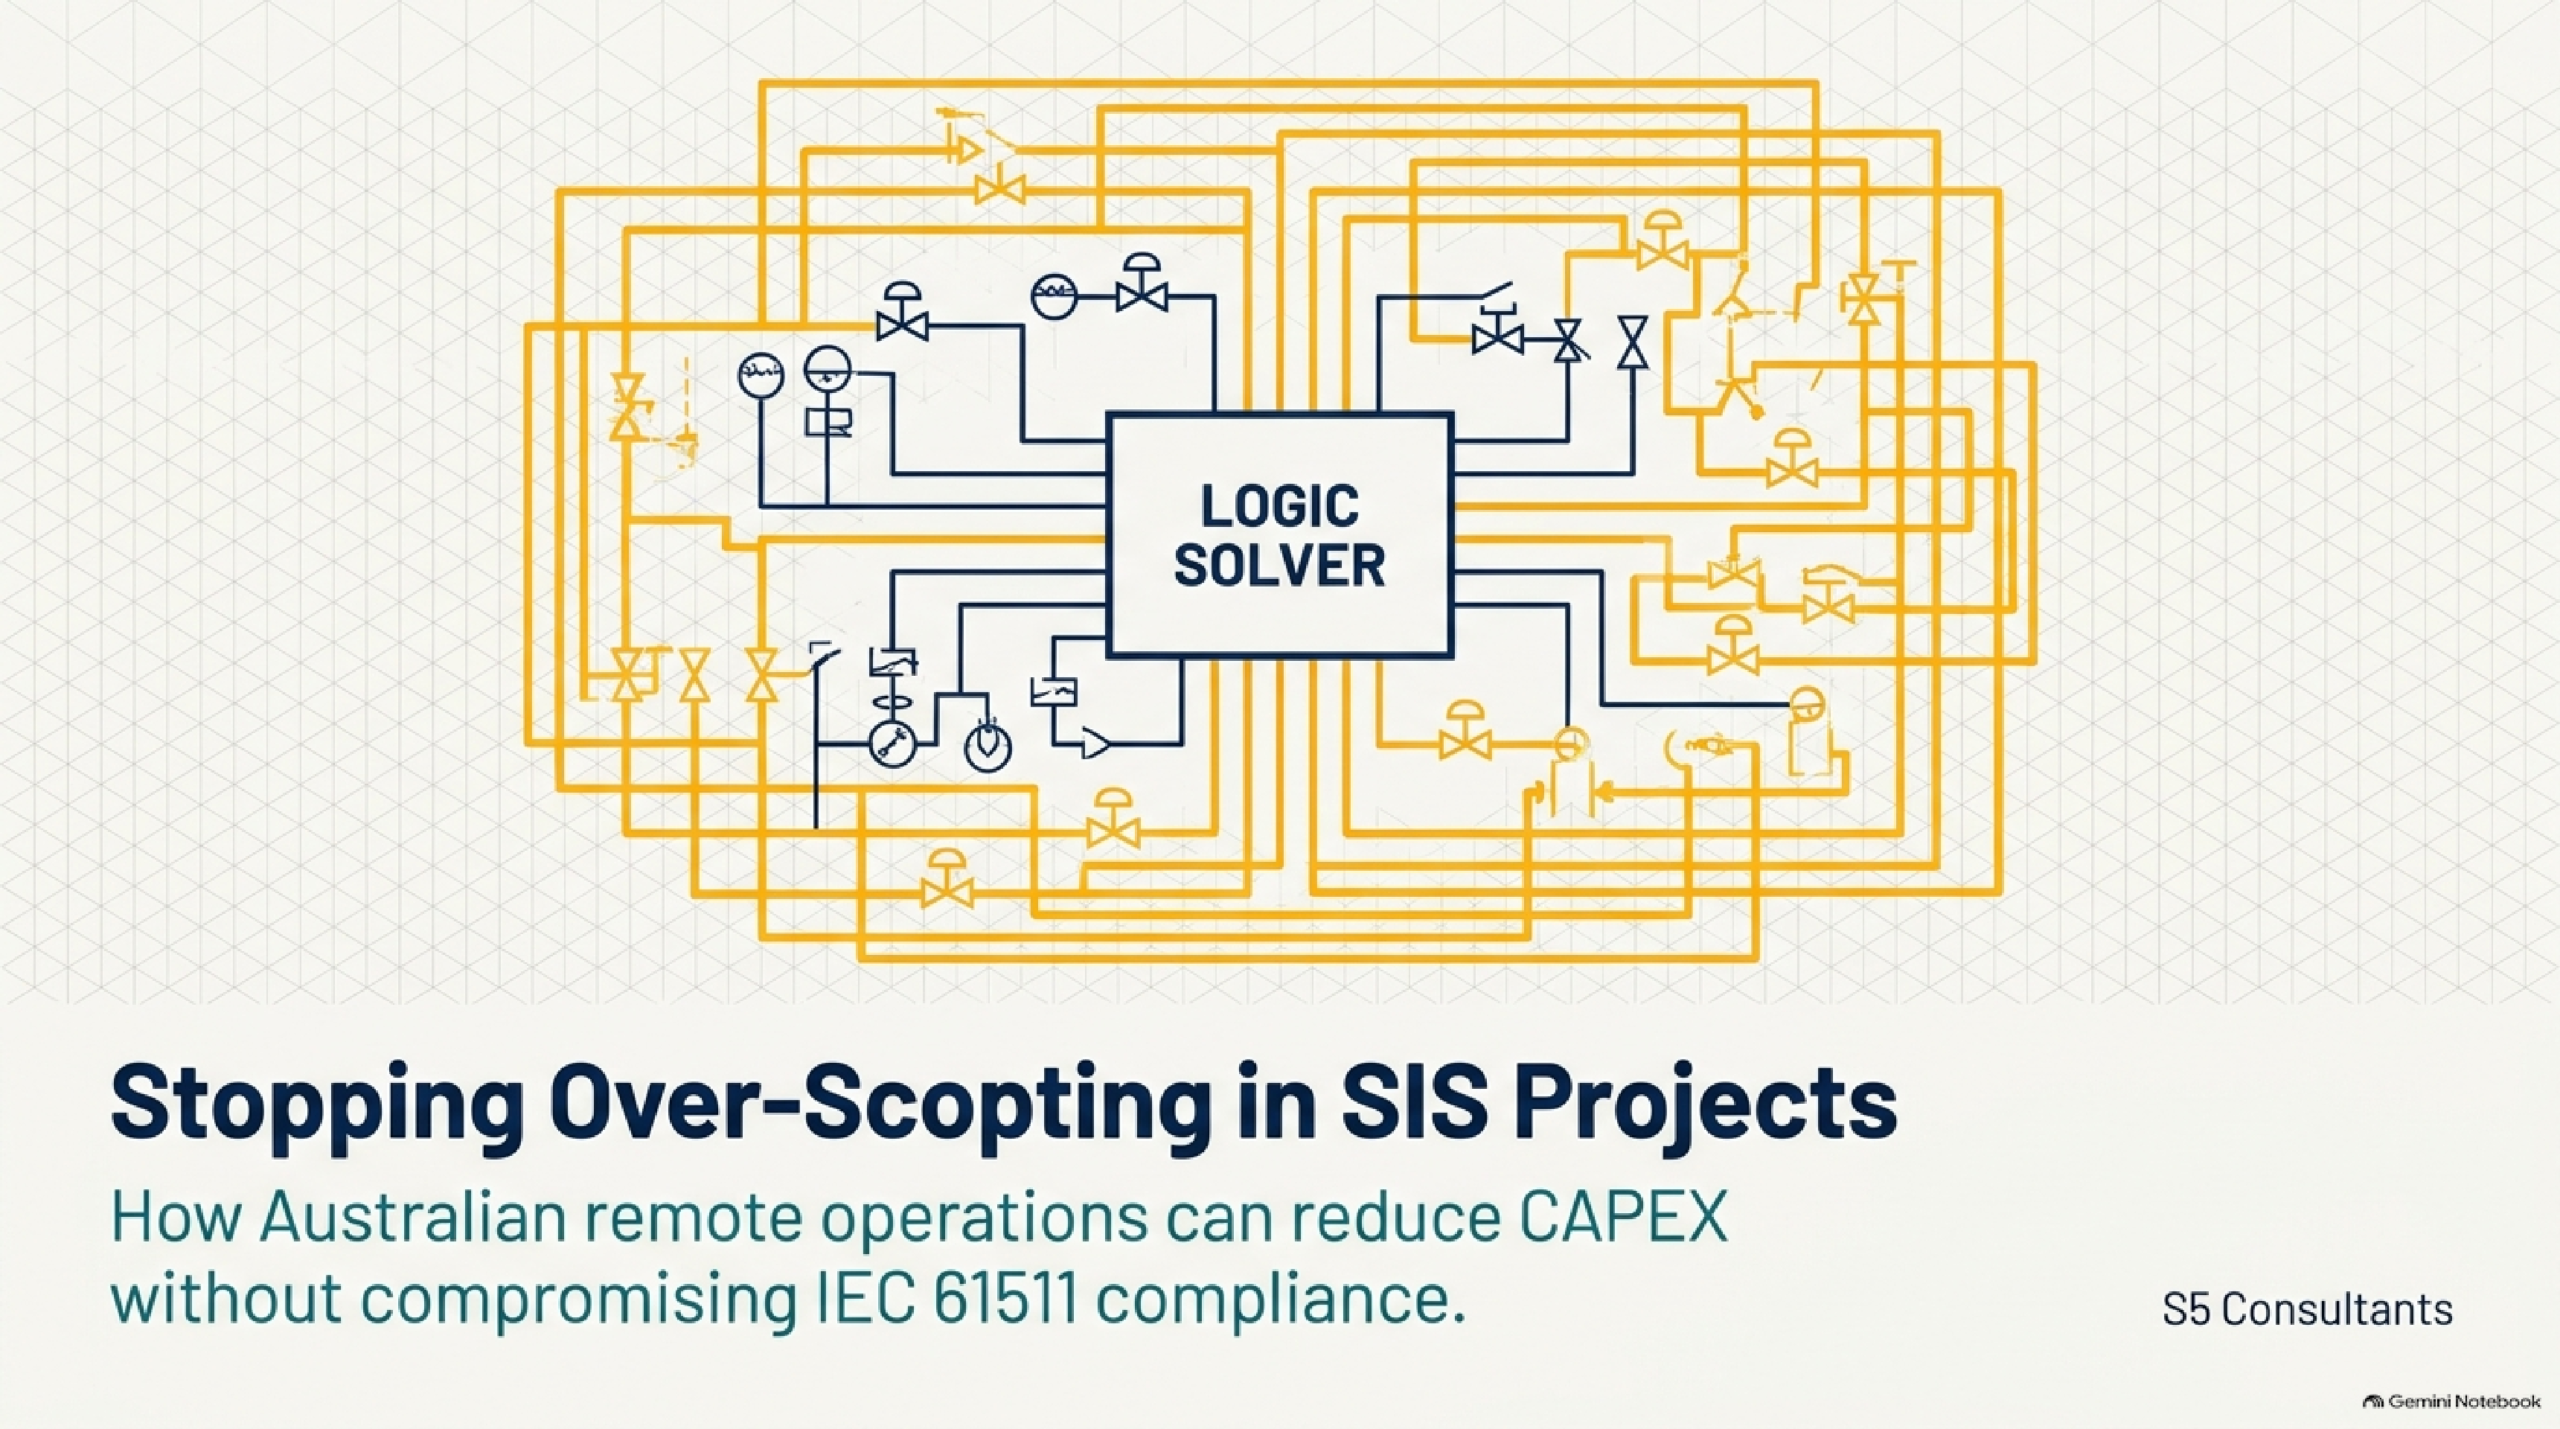
When budgets tighten or a turnaround is rushed, the pressure to share hardware, logic or
communication cards between the two domains becomes very strong. Shared components save capital
once and compromise the safety claim for the life of the plant.
How safety instrumented system independence erodes
- A spare channel on a control system card is used for a safety input because it was available.
- A safety and control network are bridged so one HMI can display both, on a segment assumed to
be segregated. - Separate physical cabinets share a common power supply, earth reference, or a backplane
believed to be independent. - A software modification is deployed to the control system and propagates into the shared
engineering environment.
None of these are visible in the loop drawing. All of them defeat the assumption on which the
SIL calculation rests.
What independence actually requires
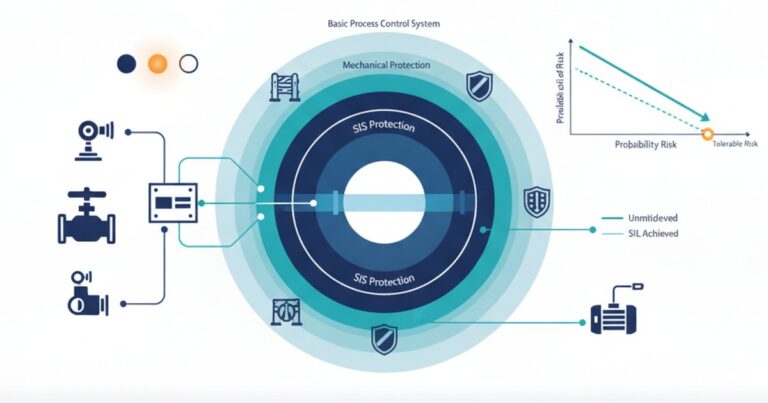
Independence is a property of the whole path, from sensor to final element:
- Physical separation of acquisition. Separate sensors, separate wiring,
separate I/O — not shared channels. - Separate logic solvers. The safety function executes on a solver that cannot
be modified by the control programme. - Separate final elements, or at minimum documented, validated common-cause
analysis where a shared final element is unavoidable. - Network segregation with evidence. Segregation that was designed but never
verified is an assumption, not a control. - Change control that spans both domains. A modification process that treats
them as one system will eventually merge them.
What an independent architecture audit delivers
- Zero safety system bypass incidents during audits.
- Around a seventy-five per cent reduction in compliance verification time, because the evidence
already exists. - Confidence during high-risk operations — turnaround, start-up, abnormal situations.
Vendor patches and tick-and-flick reviews are not enough, because separate physical cabinets can
still hide backplane dependencies and logic overlaps. The review has to follow the signal path.
Related work at S5 Consultants
Independence reviews sit alongside our
functional safety and systems engineering
services. Where control and safety networks share infrastructure, the review overlaps with
OT cybersecurity: segmentation that
protects availability also protects the integrity of the safety claim. Read more on
functional safety.
Cross-published from the S5 Consultants LinkedIn stream. Follow us on
LinkedIn for the original post.
Talk to S5 Consultants
S5 Consultants is the assurance arm of S5 — functional safety, OT cybersecurity,
SCADA and systems engineering for industrial operators.
Read more on our services or
functional safety.
Discuss your project —
book a call.
Need a defensible functional-safety position?
Independent IEC 61511 consultancy — HAZOP, LOPA and SIL assessment, SIS design review and operational readiness. Led by a Certified Functional Safety Expert.
Fixed-scope engagement, clear deliverable, no obligation.